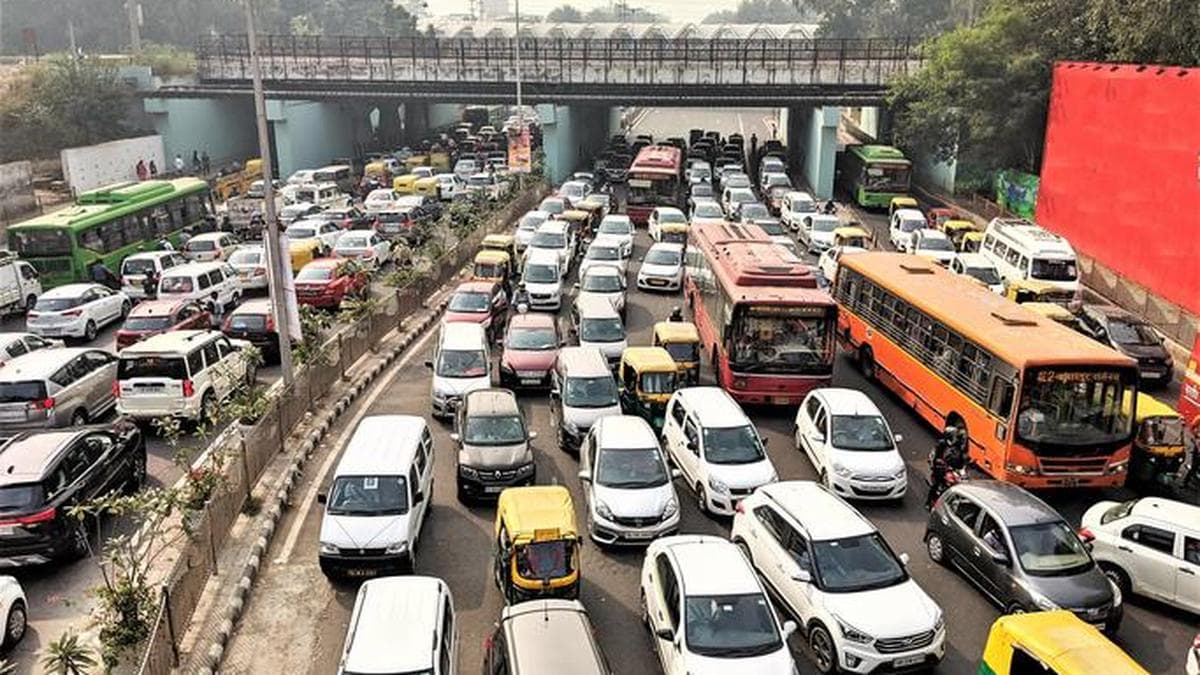
Road Ministry Orders Forensic Security Audit of Core Transport Portals Following Data Leaks
The Ministry of Road Transport and Highways (MoRTH) has directed the Indian Computer Emergency Response Team (CERT-In) to carry out a forensic security audit of its primary digital registries—VAHAN, SARATHI, e-Challan, and PUCC—after personal vehicle and driver data surfaced on illicit online channels and mobile applications. The Ministry has also sought guidance from the Ministry of Electronics and Information Technology (MeitY) to re-evaluate its data-sharing policy, while seeking removals of unauthorised platforms offering sensitive records for nominal fees.
Relevance for Governance and Cyber Security
This development is significant for discussions surrounding digital public infrastructure, privacy safeguards, and cybersecurity compliance in India. As public registries become foundational to digital governance, the incident illustrates the vulnerabilities associated with application programming interfaces (APIs), third-party data access, and data triangulation—where non-sensitive data points from separate portals are aggregated to reconstruct private identities. The case also tests institutional compliance with the regulatory principles set out under the Digital Personal Data Protection Act, 2023.
Live Test Series
Join thousands of aspirants in our weekly live mock tests. Get real-time ranking and detailed analysis.
Key Systems and Corrective Measures
- Audited Platforms: VAHAN manages national vehicle-registration records; SARATHI processes driving licences; e-Challan tracks traffic violations; and PUCC oversees vehicular emission compliance.
- Integration and Exposure: Consolidated data flows into the National Transport Repository and platforms like the Unified Logistics Interface Platform (ULIP), managed by the National Industrial Corridor Development Corporation (NICDC). Following unusually high usage—with certain approved entities logging over 50 lakh hits per month—authorities initiated inquiries into whether data access adhered strictly to authorised scopes.
- Access Framework: An RTI disclosure revealed that 25,314 credentials had been granted to private entities, resulting in 1.708 crore queries over 33 months. While private access includes masked personal identifiers and search caps, government and law enforcement bodies receive broader access.
- Strengthened Controls: Going forward, government agencies seeking repository access will require approval from the Transport Secretary, coupled with Aadhaar-based digital signatures or video KYC, alongside mandatory CERT-In security audit certification.
Reported by The Hindu — National
Related Test Series
12th BRICS Parliamentary Forum Held in New Delhi Emphasising Multilateral Dialogue and Reform
Oct 26, 2026
IIT Madras Study Examines Unequal Labour Market Impacts of Artificial Intelligence in India
Oct 26, 2026

Houthi Missile Attacks Target Saudi Infrastructure Amid Escalating West Asian Regional Conflict
Oct 26, 2026
Resolving Pricing and Structural Challenges in India's Sugarcane and Sugar Milling Sector
Oct 26, 2026
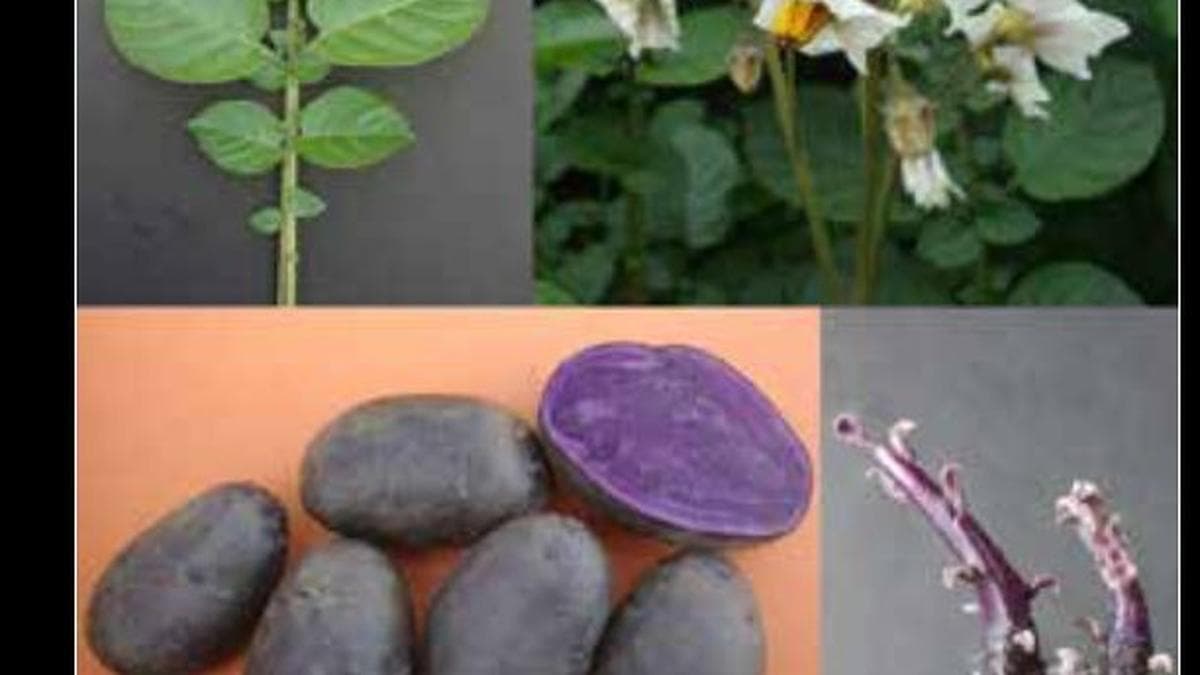
ICAR-CPRI Develops 'Kufri Jamunia' Biofortified Potato to Tackle Hidden Hunger
Oct 26, 2026